
Agentic AI Governance: A Practical Guide to Controlling Autonomous AI in the Enterprise
Summarize and save time
Traditional AI systems have evolved from the mere task of answering questions to taking action with agentic AI systems. Traditional AI systems summarize documents, classify tickets, and provide product recommendations. But when it comes to agentic AI services, they can do much more by taking a step further and planning actions, retrieving information, extracting information from relevant tools, updating records, triggering workflows, coordinating with other AI systems and agents, and so on.
As this transition is evolving and creating significant business value, there is also the rising risk of governance with this shift. When AI systems act autonomously and connect with CRM, ERP, and other data systems, there is an increased threat to the information they convey and the actions they take. These need to be controlled with well-planned agentic AI governance frameworks.
Agentic AI governance refers to the framework used for defining, enforcing, monitoring, and maintaining the authority permitted to autonomous AI agents. It determines what the AI agents can do, what data access they can have, which tools they can use, which decisions require human approval, and which of their actions are logged, monitored, and evaluated.
The goal is not to overcome or eliminate the independent functioning authority of these systems, but to control and measure their autonomy to reduce business risks.
Market Statistics for Agentic AI Governance
- Gartner forecasts that by 2028, 33% of enterprise software applications will include agentic AI.
- The global agentic AI market is expected to witness a CAGR of 40.2%, with projections estimated to reach USD 205.88 billion by 2033.
- Data from McKinsey research indicates that 62% of organizations are experimenting with AI agents, but only 23% are scaling agents in at least one business function.
- According to Gartner reports, more than 40% of agentic AI projects might get cancelled by the end of 2027 due to rising costs and inadequate risk controls.
What is Agentic AI Governance?
Agentic AI governance refers to the structured management of delegated authority for autonomous AI systems. It ensures risk control and security of the systems by defining what the AI agent can access, finalize, and execute when operating on behalf of your business.
| Traditional AI Systems | Agentic AI Systems |
|---|---|
| Focused on the model output. | Focuses on what the agentic AI systems can do to ensure a controlled autonomy. |
| Identify if the model is accurate. | Defining what the agent can do. |
| Ensuring that the output is not biased. | Stating what data and systems it can access. |
| Protecting sensitive business data. | Outlining how its behavior will be monitored. |
| Determining whether or not the decision can be explained. | Mentioning the actions that will require human approval and who will be accountable for unforeseen results. |
| How to stop or pause the functioning of the AI agent. |
Make a strong agentic AI governance strategy part of your broader AI development services with Prakash Software Solutions Pvt. Ltd. (PSSPL). Partner with us for end-to-end development ownership, where we identify your data readiness, agent architecture, security policies, and monitoring support before outlining the development roadmap. Our team of 250+ AI experts and engineers conduct a thorough evaluation of your project requirements, market dynamics, and target audience expectations to customize aligned agentic AI services.
Difference Between Agentic AI Vs. Traditional AI Governance
Let's look at a side-by-side comparison of agentic AI governance and traditional AI governance in detail:
| Focus Area | Traditional AI Governance | Agentic AI Governance |
|---|---|---|
| Primary Focus | Predictions and model output. | Delegated authority of the tools and agent actions. |
| Identity and Access Control | Data access with user or application identity. | Access to data, tools, workflows, systems, and APIs with user plus agent identity. |
| Core Question | Is the output secure, accurate, and compliant? | Is this action authorized within the defined scope? |
| Role of Human Agent | Reviewing outputs. | Supervise, approve, override, and intervene in the actions of agentic AI systems if it's beyond their stated access control. |
| Risk and Monitoring | Monitoring the model performance to identify any bias and data risks. | Monitoring runtime behavior and action trails of the system to identify potential security, delegation, and operational risks. |
| Failure Response | Model correction. | Rollback, suspension, and recovery. |
Why is Enterprise AI Governance Needed?
Just like the significant value created by AI agents, the risk level is also created quickly. Risks can be in various forms, like an AI agent might modify a record when it’s only permitted to retrieve it. Or an AI agent that is meant to prepare and submit reports might access data that it must not see.
Risk issues when it comes to enterprise AI governance are not always malicious attacks. They can result from undefined scope, weak integrations, excessive permissions, evolving data, and poor workflow design. Here are a few compelling reasons that make agentic AI governance the need of the hour:
Irreversible Agent Actions
Some actions are such that they can’t be easily undone or reversed. Some actions with immediate consequences include:
- Modifying access permissions
- Updating a financial record
- Transaction approval
- Deploying code
- Sending a customer communication
Agents Have Access to Real Systems
Every startup and enterprise looks to build AI agents that can seamlessly and securely connect with APIs, CRMs, ERPs, databases, email services, cloud platforms, and existing internal tools and systems. While this access makes them useful, it also expands the potential risks.
Unclear Accountability
In instances where an AI agent takes an unauthorized action, the accountability can be either with the model provider, system integrator, business owner, platform operator, or the organization deploying it. To avoid this uncertainty, it’s vital to define accountability before deployment, and agentic AI governance helps with that.
Increased Complexity Resulting from Multi-Agent Workflows
When work is passed from one agent to another, context and permission flow also expand. For example, a small error by one agent can become a reliable input for the other, causing a substantial workflow failure.
Behavioral Drift Over Time
AI agent development services are implemented in evolving environments where data constantly keeps changing, tools are updated, prompts are modified, workflows expand, and business rules evolve. In such cases, enterprise AI governance helps detect drift before it becomes a pressing security or operational risk.
Build Agentic AI Governance from the Onset
Agentic AI systems are not to be governed only after the agent reaches the production and deployment stage. Governance needs to be built from the start into the agent’s identity, permissions, tool access, workflow design, monitoring, and human-approval rules.
As a responsible enterprise AI development company, at PSSPL our experts assist enterprises to assess AI readiness, define the agent restrictions, and design agentic systems that are governed and aligned with your business goals and security protocols.
Core Components of Agentic AI Governance Framework
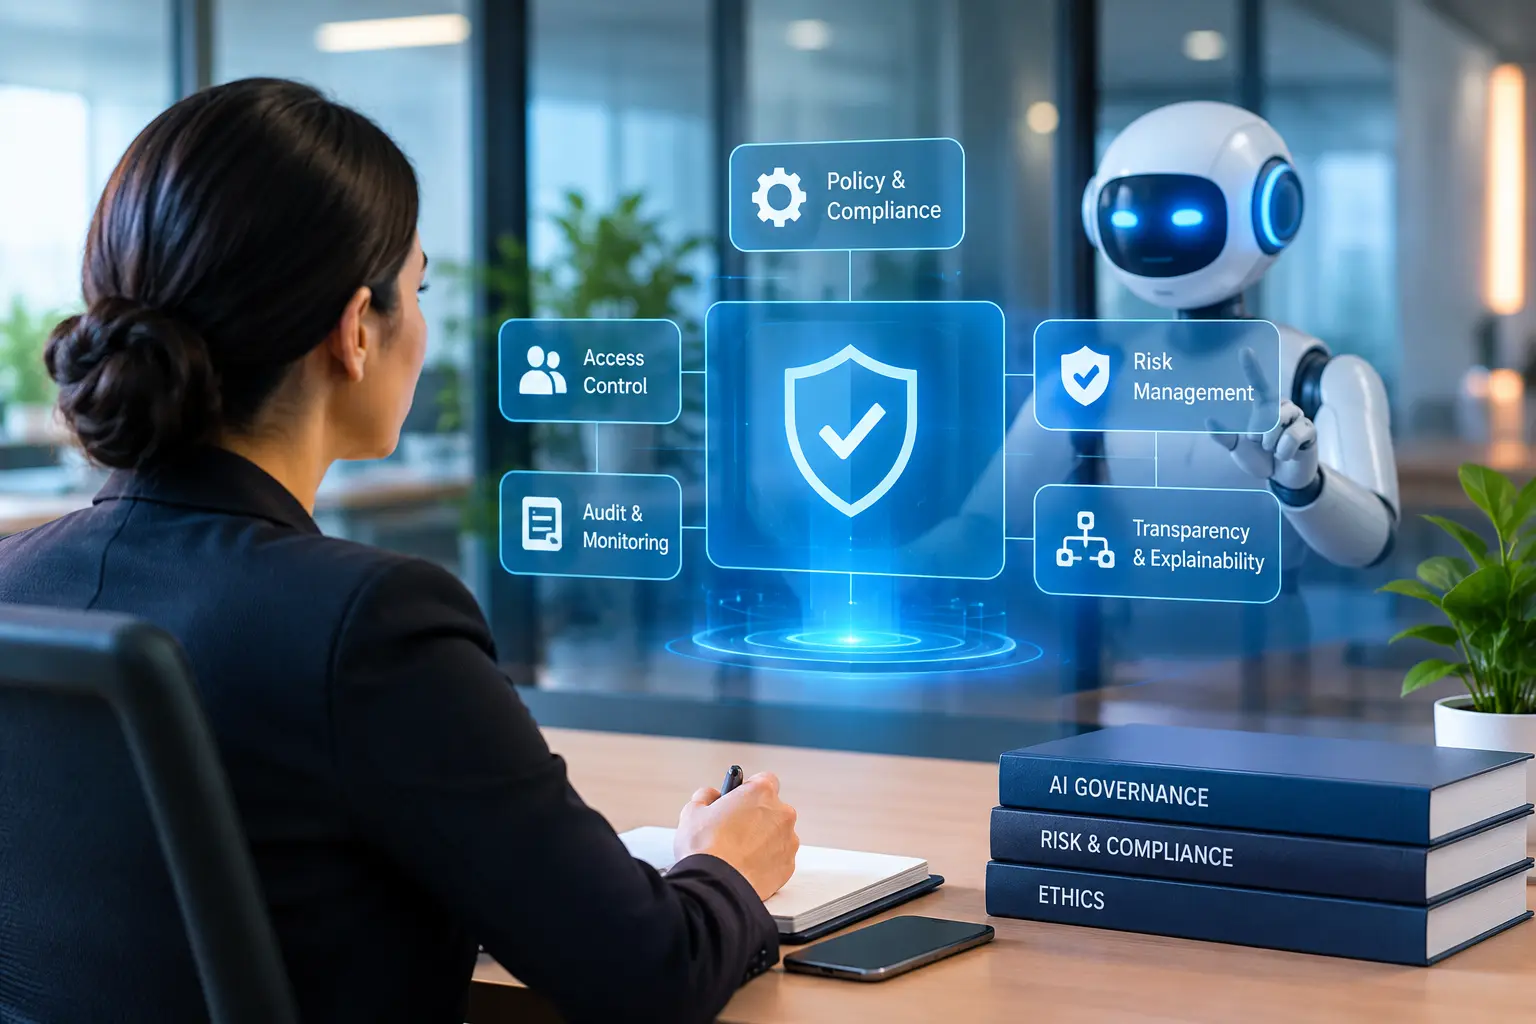
An effective enterprise AI governance framework for agentic AI systems is one that includes distinct components, each serving a different purpose. Let’s look at some of the core components of the agentic AI governance framework:
-
Agent Identity and Ownership
Every AI agent system meant for production needs to have a unique identity, defined scope, and accountable owner. Clear identity management is vital, especially for organizations considering scaling AI agents, without which reliable management of permissions, access revocation, or audit actions can’t be done.
This component includes:
- A well-documented business process
- A unique agent
- A named business or technical owner
- A record of approved capabilities, integrations, and dependencies
-
Agent Inventory and Classification
An organization should maintain an inventory of all AI agents, and each agent should be classified based on autonomy and risk. For instance, a research-only agent needs fewer controls compared to an agent responsible for modifying financial records.
This component includes:
- Data sources and permissions
- Tools and APIs
- Business and technical owner
- Agent name and purpose
- Autonomy and risk classification
- Monitoring status
-
Approved Tools and Data Sources
Agentic AI governance must also clearly define which tools and business data the agent systems can use and access. Accessing data or tools outside of these specifications should be prevented by the governance framework.
This component includes:
- Approved databases and APIs
- Approved document repositories
- Approved external services
- Approved knowledge sources
-
Least-Privilege Access
The access granted to the agentic AI services must be restricted to their approved purpose. For instance, a customer support agent can read order details and create a support ticket. But it can’t change pricing, approve refunds, or access irrelevant customer records.
This component applies to:
- Cloud resources
- Databases and APIs
- Internal applications
- Documents and payment systems
- Email and messaging tools
-
Runtime Policy Enforcement
Governance policies must be implemented when the agent is operating and not only during periodic reviews. For instance, a procurement agent can create a purchase order below a defined value, and anything above that should mandate human approval.
Runtime controls can:
- Check permissions
- Restrict data access
- Validate tool calls
- Apply business rules
- Require approvals and trigger escalation
-
Observability and Audit Trails
Every agent action that adds value should be traced, as this information assists in debugging, compliance, security testing, and continuous improvements.
Audit logs must capture:
- User requests and agent identity
- Retrieved information and accessed data sources
- Model output and tool calls
- Approval decisions
- Final outcome
-
Human Oversight and Approval Gates
The need for human oversight should be directly proportional to the risk level. For low-risk actions, they can run automatically within stated limits. For high-risk actions, human approval should be compulsory.
Examples of actions where human approval would be required include:
- Changes in access
- Financial transactions
- Contract approvals
- Processing customer refunds
- Production deployments
- Policy cancellation
-
Incident Response
Agentic AI governance should also state what happens when an AI agent behaves unexpectedly. Enterprises should clearly establish:
- Who can pause the agent and revoke access?
- Who can roll back changes?
- The way lessons are documented
- The way customers or stakeholders will be notified
- Incident investigation and the way the agent is restored safely
Key Risks of Ungoverned AI Agents
A lot of enterprises make the mistake of not having a defined enterprise AI governance framework for agentic systems. This lack of governance can result in the following challenges:
-
Unauthorized Tool Calls
An agent system might end up calling a tool that was not needed for the specific task. This happens when permissions are too broad or in the case of unconstrained tool selection.
-
Excessive Permissions
To be safe, agents are sometimes given broader access. This creates a large risk if the agent makes an error; the security is compromised, or it is used outside of the defined scope.
-
Prompt Injection
Untrusted content might be processed by agents from documents, emails, web pages, and retrieved records. If there are any malicious instructions hidden in that content, it can have a potential impact on the agent’s behavior.
-
Data Exposure
Sensitive data can be exchanged between systems by the agents. In the absence of clear data-flow controls, confidential information might be leaked to users, systems, or third-party services that are not meant to have access.
-
Accountability Gaps
If there is no proper specification of who owns the agent, permissions, or its outcomes, an effective response when something goes off track is not possible.
-
Cost Overruns
Agents may frequently retrieve large documents or execute inefficient workflows. In such cases, no monitoring can sharply raise operating costs.
Successful implementation of Agentic AI Governance
If you are considering how to implement agentic AI governance, you need a strategic plan in place to ensure its success. And for this, you need experienced enterprise AI development companies like Prakash Software Solutions (PSSPL).
At PSSPL, we ensure successful implementation of agentic AI governance with the following process:
(1) Begin with a Defined Business Use Case
Don’t make the mistake of starting by choosing a generic model or platform. Begin with a workflow that defines a clear business owner, measurable outcome, and manageable risk. Our goal is to understand your workflow and then decide which AI agent model will be more appropriate.
(2) Assessing Data and Integration Readiness
We then review the data sources, APIs, existing systems, and workflows needed by the AI agent. This helps us evaluate the integration readiness by answering key questions like:
- Data accuracy and relevance
- The data owner
- Identifying sensitive data and the systems that need to be connected
- Availability of APIs
- The permissions required
- What happens if the integration fails
(3) Defining Agent Scope and Limitations
In this stage, we document the purpose and limitations of the AI agent systems to provide clarity about their autonomy. For instance:
- The agent can create a customer support ticket.
- The agent can send a status update.
- The agent can’t issue refunds or modify customer records.
- The agent should escalate legal or financial disputes to human agents when needed.
(4) Classifying Autonomy and Risk
Design a risk tier for each agent labelled as low, medium, high, and critical. With each risk level, also state the subsequent governance approach.
(5) Implementing Identity and Permission Controls
For each agent, we assign a separate unique identity and apply least-privilege access with separate permissions to read, write, approve, and execute actions.
(6) Testing Before Deployment
At PSSPL, before the full-scale launch of an AI agent system, we always test and monitor its appropriateness and performance with real-time scenarios. This includes testing for:
- Unauthorized requests
- API failures
- Normal requests
- Incomplete data
- High-risk actions
- Conflicting information
(7) Regular Review and Monitoring
We provide an end-to-end development partnership, which means we also offer ongoing support and maintenance of the AI agent systems. This includes tracking user behavior, access permissions, performance, cost, user feedback, data sources, and level of autonomy.
How to Choose an Enterprise AI Development Company?
To ensure accurate, reliable, and secure performance of the AI agents and to scale them as the business needs evolve, choosing the right enterprise AI development company is very important. A reliable partner is one who helps you eliminate overengineering and recommends the simplest system architecture that aligns with your budget, business needs, and user expectations.
You can evaluate the providers based on their:
- Experience with AI agents and multi-agent systems.
- Data engineering and RAG expertise.
- Integration ability with CRM, ERP, cloud platforms, and legacy systems.
- Delivery and engagement models.
- Long-term support and maintenance.
- Governance and compliance policies.
PSSPL ranks as a leading enterprise AI development company among global brands for our end-to-end development support. From strategizing and agent architecture to designing, deployment, enterprise integration, security, monitoring, and post-deployment optimization, we take care of everything. We use cutting-edge technologies to build and deploy enterprise-grade AI agent development services.
Why Partner with PSSPL for Agentic AI Governance?
As a 26+ year old AI app development company, we have a team of 250+ AI engineers and experts catering to 500+ global clients across 40+ countries. Our track record of successfully delivering 1000+ enterprise projects globally ensures unparalleled excellence in our AI development services.
We provide full-scale AI development, including:
- Enterprise AI development
- Agentic AI services
- AI agent development
- Data engineering
- Cloud computing
- Governance-focused AI implementation
- NLP
- Computer vision
- Generative AI
- Predictive modeling
- AIOps
From discovery and readiness assessment to secure development, deployment, and maintenance, our team of experts is with you throughout the agentic AI governance cycle.
Get a Practical Agentic AI Governance Roadmap
If you are planning AI agent development services, your next step isn’t to deploy more tools. It’s to find the right partner who can help you automate workflows, understand what data and systems are involved, and implement strict enterprise AI governance for the agentic AI systems.
Design a practical agentic AI governance roadmap with PSSPL to balance innovation, security, compliance, and measurable ROI.
Frequently Asked Questions (FAQs)
Agentic AI governance refers to the framework used to control the autonomy of AI agents. It covers aspects such as agent identity, permission control, data access, tool usage, autonomy, human oversight, monitoring, security control, and accountability.
Enterprise AI governance is essential to control what the autonomous AI agents can do, what data they can access, what tools they can use, what decisions they can take, and what actions they can execute with limited human intervention. Governance helps to manage security, operational risks, compliance, cost, and accountability.
Key controls to govern agentic AI services include:
- Least-privilege permissions
- Approved tool access
- Unique agent identity
- Human approval gates
- Audit trails
- Periodic risk reviews
- Security monitoring
At PSSPL, we monitor an AI agent based on its actions, tool calls, model outputs, data access, workflow, cost, and policy violations. This is done by using dashboards, alerts, periodic reviews, and audit trails.
The frequency of reviewing AI agent development services completely depends on the level of risk and autonomy. High-impact agents require more frequent reviews compared to low-risk agents. At PSSPL, as a responsible enterprise AI development company, we believe that all production agents should have constant monitoring and periodic formal reassessments.
We ensure agentic AI governance at PSSPL by helping enterprises to:
- Define the AI agent scope
- Building secure architecture
- Implement strict access permissions
- Seamless integration of enterprise systems
- Designing human-approved workflows
- Establishing monitoring and maintenance of agents post-launch
Final Thoughts
Agentic AI governance is not meant to slow innovation by controlling the autonomous capability of AI agents and systems. It’s simply about making innovation and automation safe, smart, reliable, secure, measurable, and scalable.
Don’t treat this as a compliance checkbox. Rather, be smart enough to implement it into the agent architecture from the beginning with reputed enterprise AI development companies like us. With the right governance foundation, we at PSSPL help businesses confidently transition from AI experiments to production-ready agentic systems that deliver real value while safeguarding sensitive business and user data.
I have managed SEO and digital campaigns in several industries, but the industries that have really benefited have one thing in common; the traffic we are driving is the right traffic, and each rupee spent relates to an actual business goal. It is easy to rank for a keyword and get clicks, but the challenge comes in when we need to ensure that these visits convert, and the team knows from which medium the visit came. It is here where most "set and forget" campaigns fail, and it is here where we concentrate most of our efforts.